SuperMokh
Bahtera 3108 2025 web writeup for SuperMokh, escalating a guest session to admin by modifying and replacing a JWT authentication token.
Challenge Overview
- Challenge: SuperMokh
- Category: Web
- Points: 100
- Historical challenge URL:
https://supermokh.bahterasiber.my/
Di padang hijau berlari laju, SuperMokh gol tiada terhenti, Walau zaman sudah berlalu, Adakah anda peminat sejati?
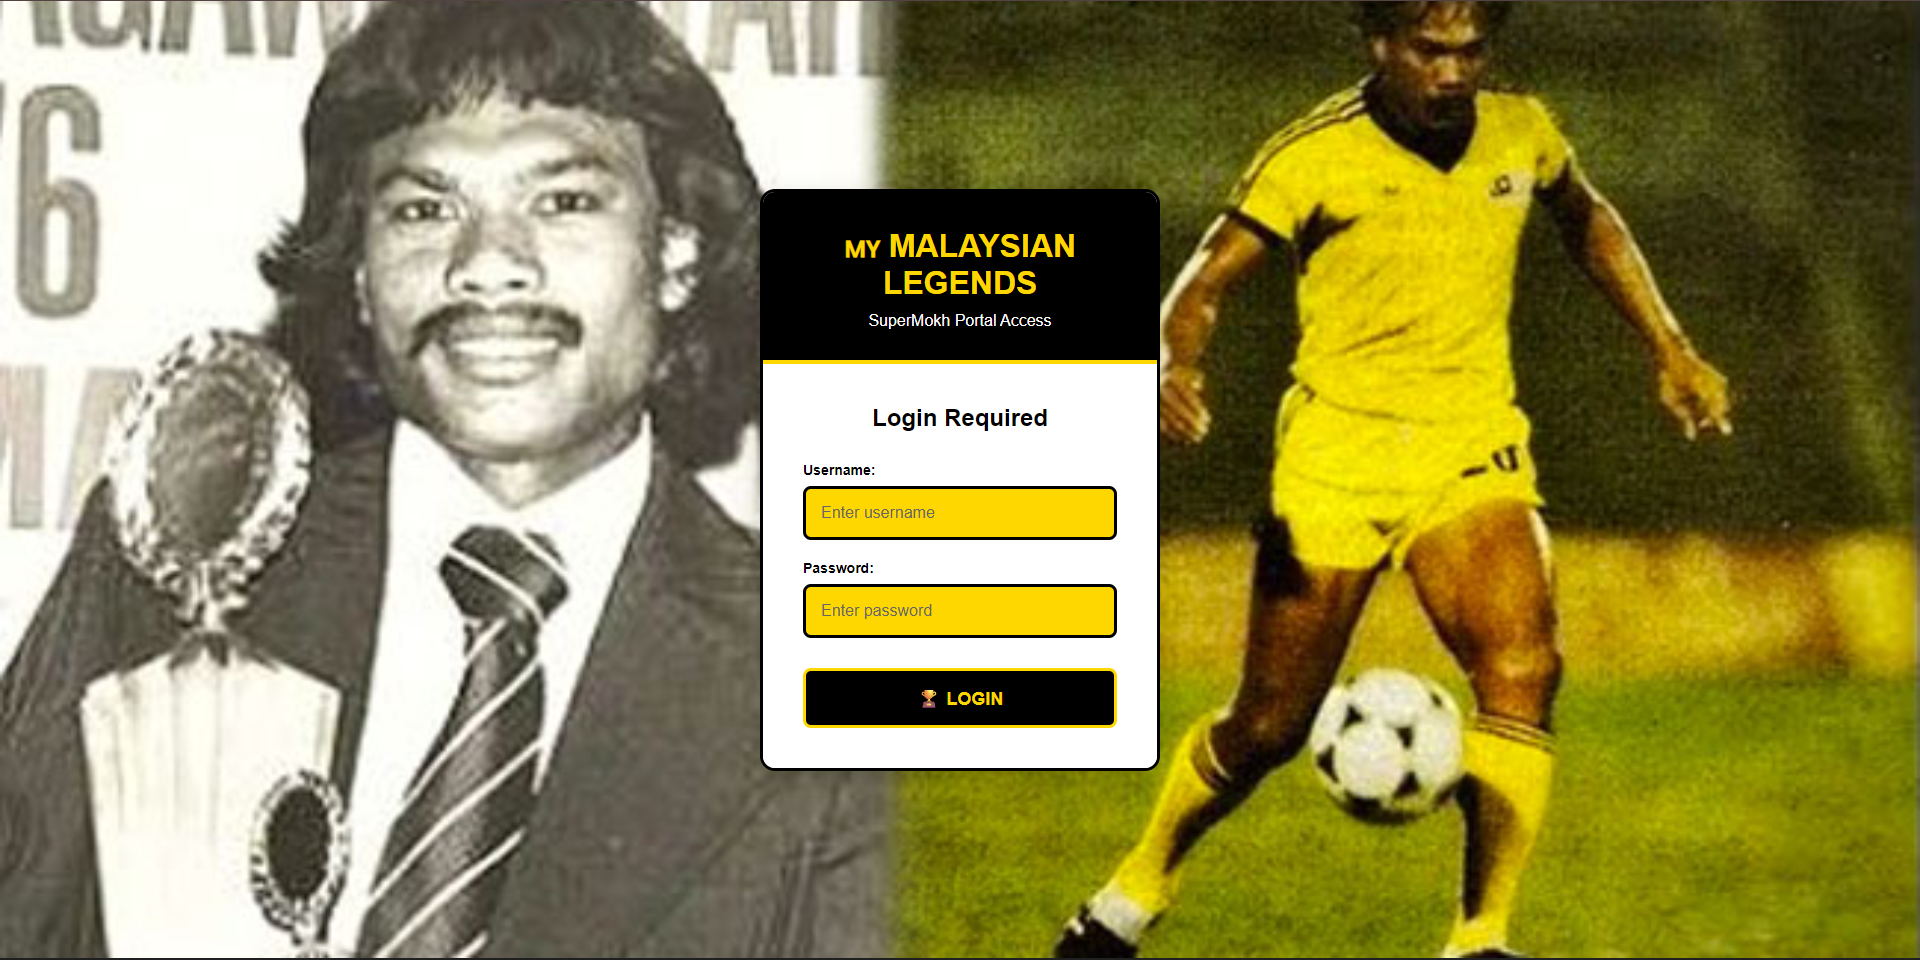
Viewing the page source reveals a Base64-encoded comment.
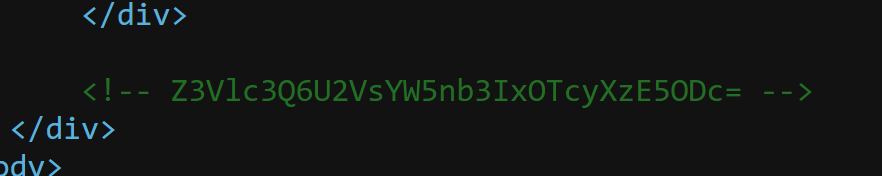
Log In as Guest
Decoding that value reveals the credentials:
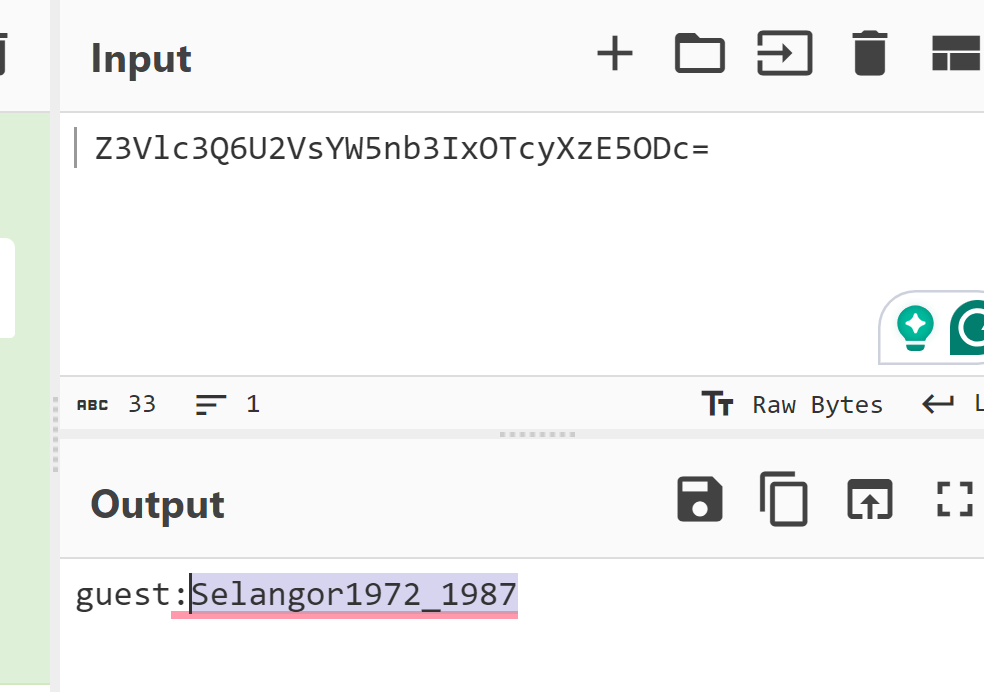
Username: guest
Password: Selangor1972_1987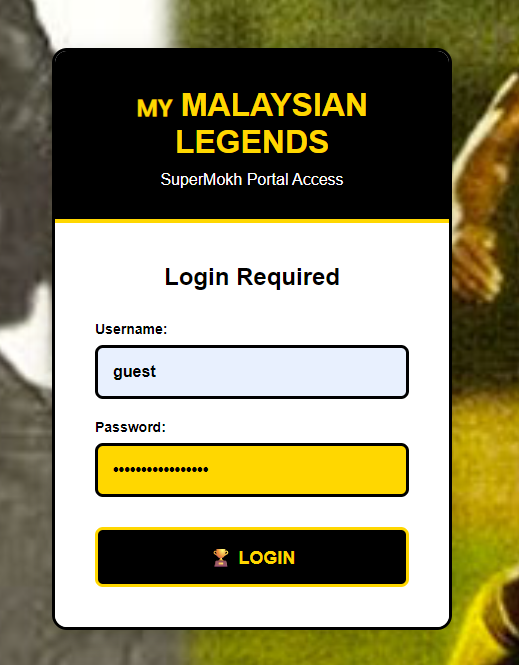
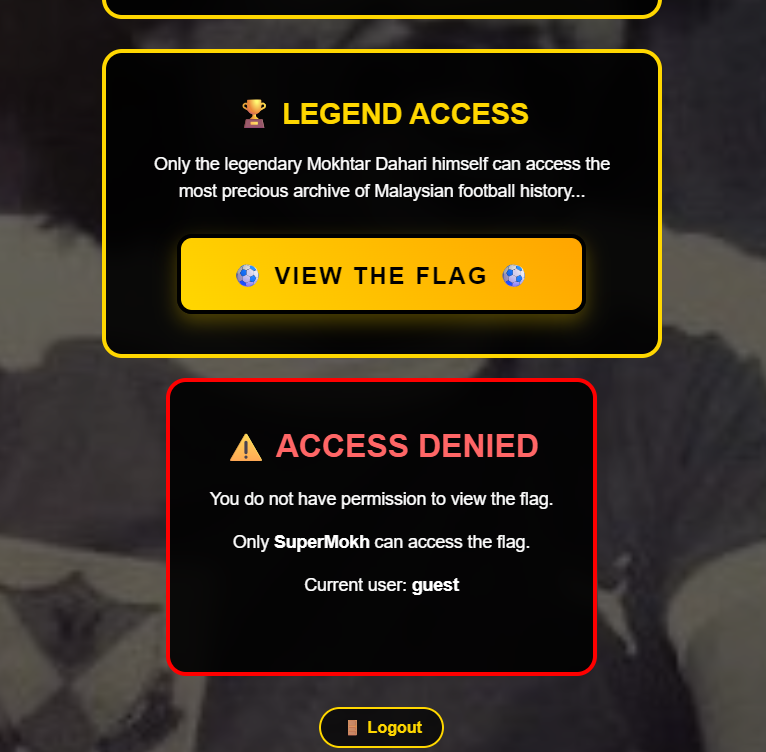
The guest account can reach the flag view but receives an access-denied message because only SuperMokh is permitted.
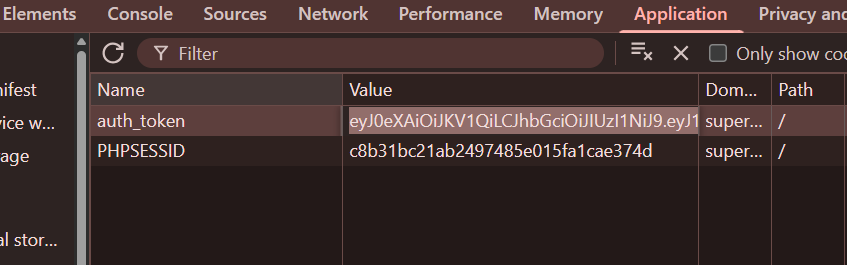
Modify the JWT
Open the authentication token in jwt.io. Decode it, then change the username and role to the following values:
{
  "username": "SuperMokh",
  "role": "admin",
  "iat": 1756887574,
  "exp": 1756891174
}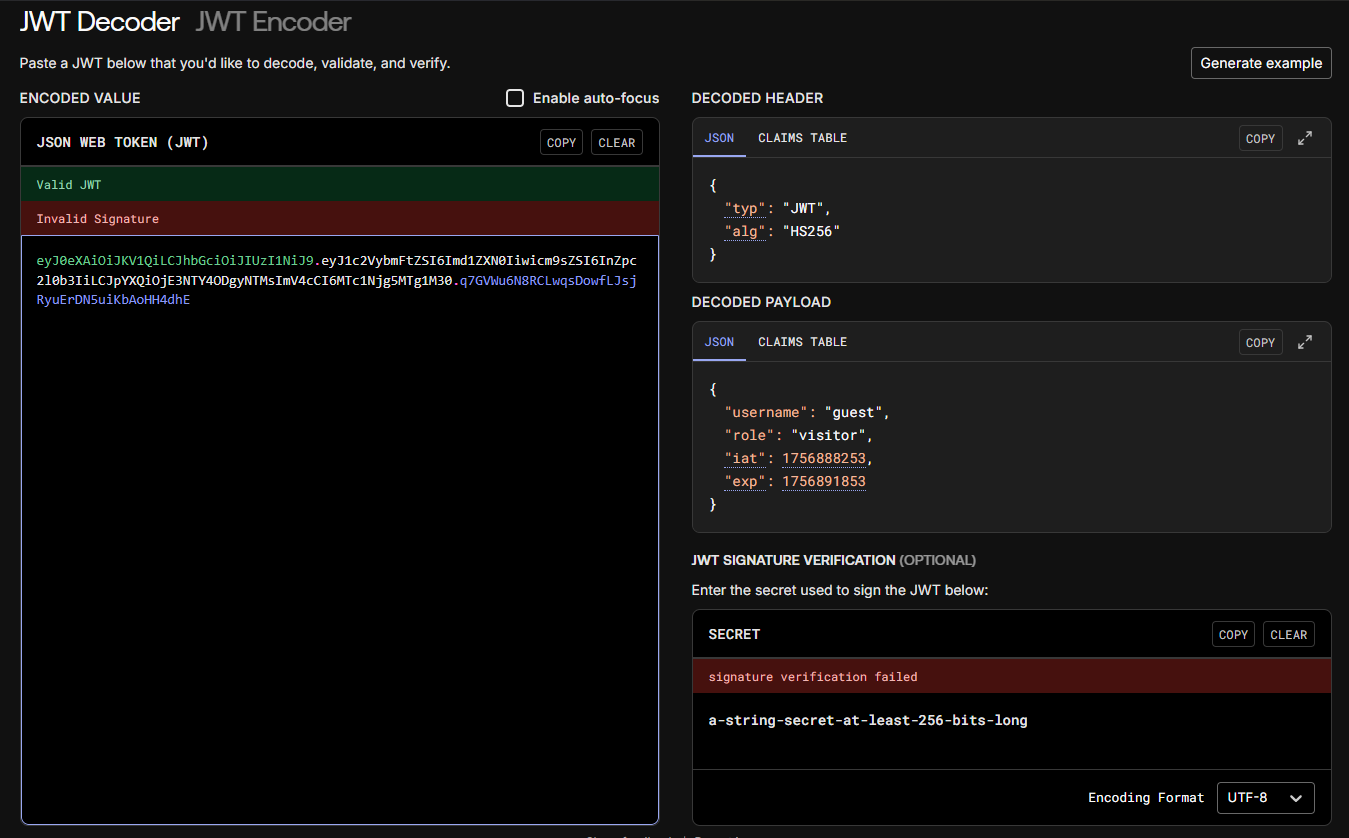
Encode the modified payload to obtain a replacement token.
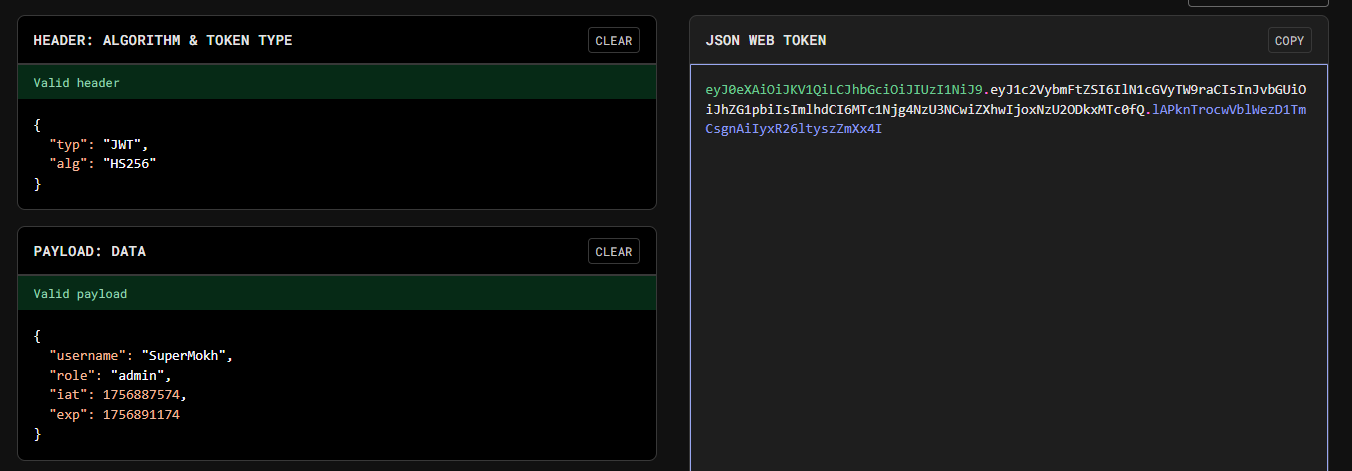
The challenge artifact records this new auth_token:
eyJ0eXAiOiJKV1QiLCJhbGciOiJIUzI1NiJ9.eyJ1c2VybmFtZSI6IlN1cGVyTW9raCIsInJvbGUiOiJhZG1pbiIsImlhdCI6MTc1Njg4NzU3NCwiZXhwIjoxNzU2ODkxMTc0fQ.lAPknTrocwVblWezD1TmCsgnAiIyxR26ltyszZmXx4IReplace the browser’s existing token with this value, refresh the page, and return to the protected view to display the flag.
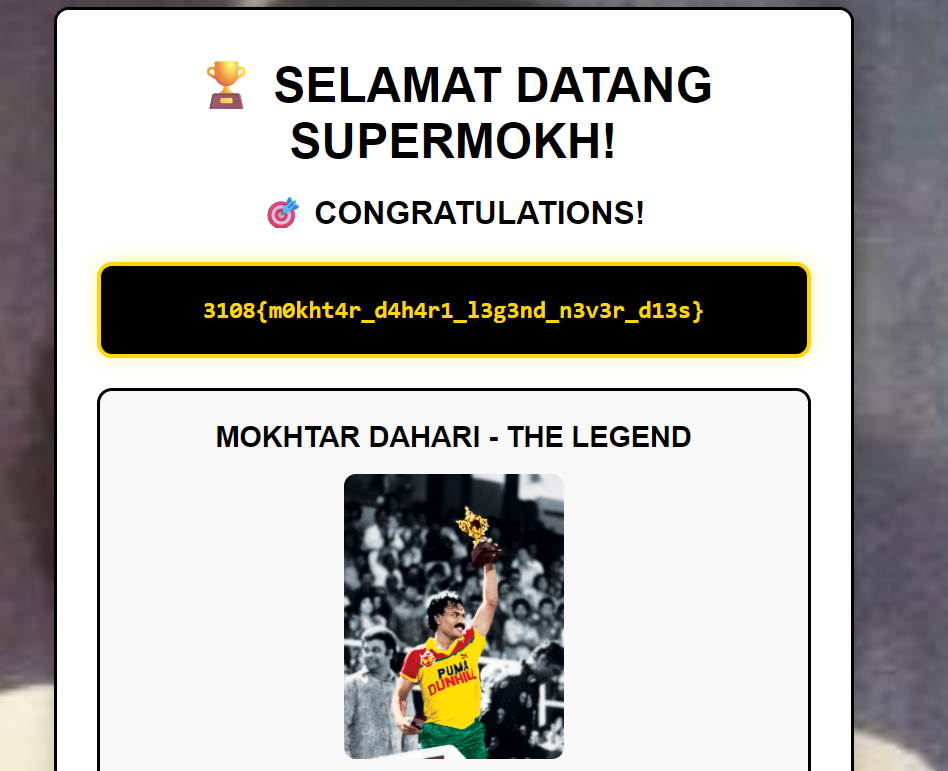
Flag
3108{m0kht4r_d4h4r1_l3g3nd_n3v3r_d13s}Related Writeups

Authorized security practice only. These notes are for lab, CTF, and explicitly permitted environments.