COMMANDer
Bahtera 3108 2025 web writeup for COMMANDer, inspecting the pilihan API response and submitting the recovered command to the check endpoint.
Medium #ctf#bahtera-3108#web-exploitation#api
Challenge Overview
- Challenge: COMMANDer
- Category: Web
- Points: 100
Terminal lama ini menyimpan biodata seseorang bersama rahsianya. Namun, rahsia itu hanya akan terbuka kepada mereka yang tahu menggunakan arahan yang tepat. Mampukah anda menguasai terminal ini untuk membongkar kebenaran?
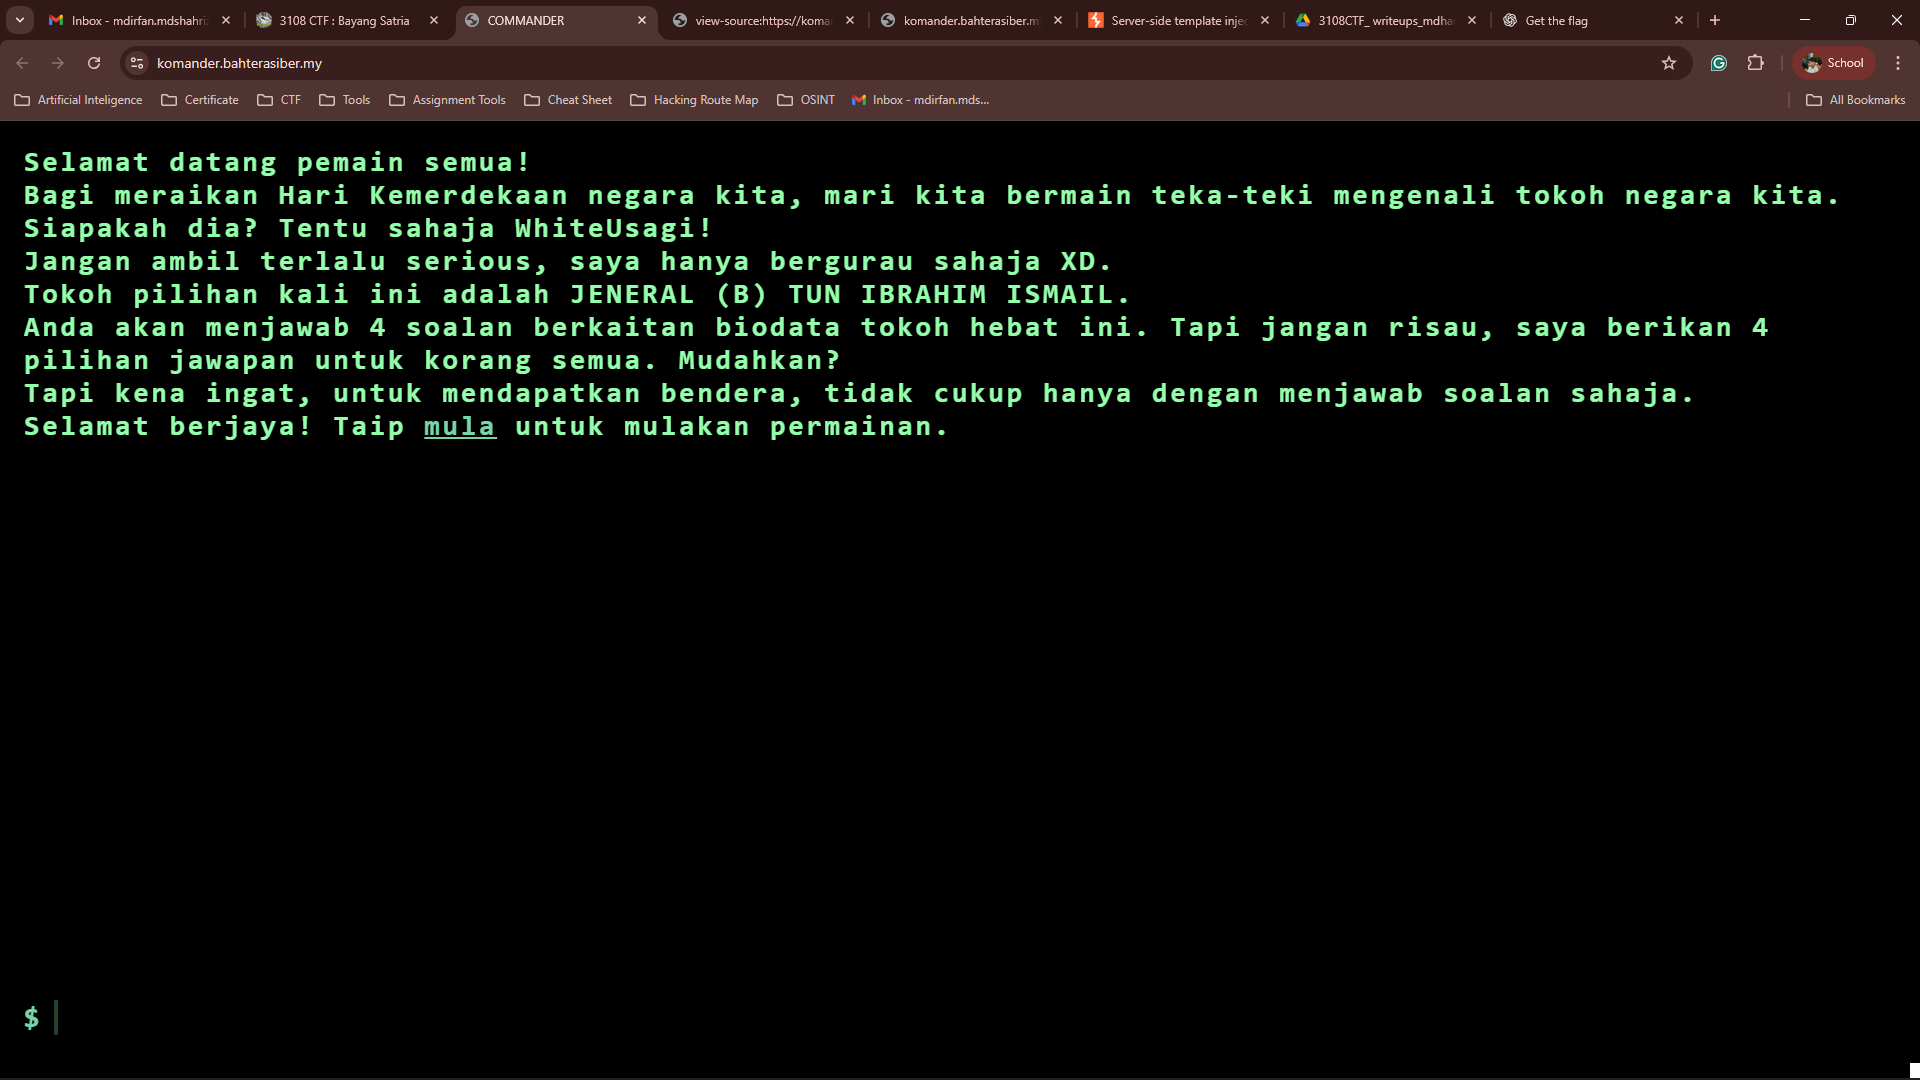
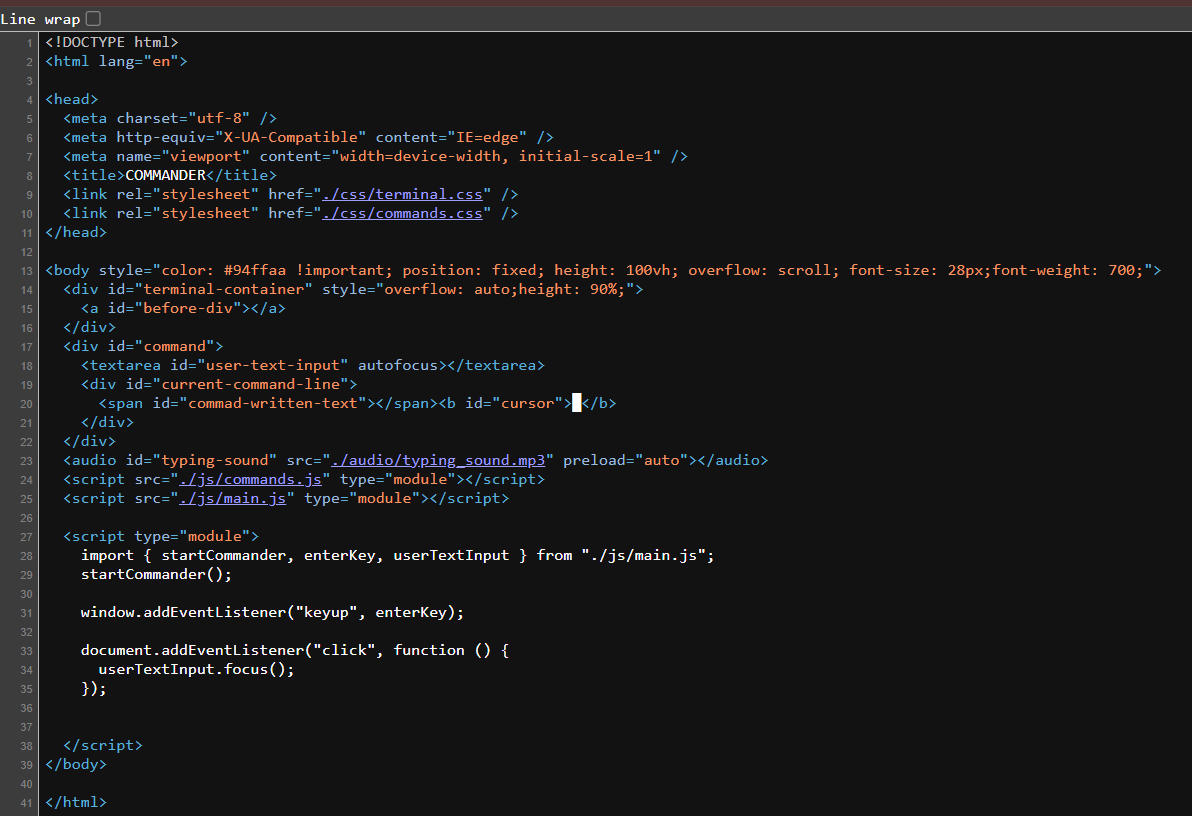
Inspect the API
Open the browser’s developer tools, select the Network tab, refresh the page, and inspect the request to /api/pilihan. The required value is present in its JSON response.
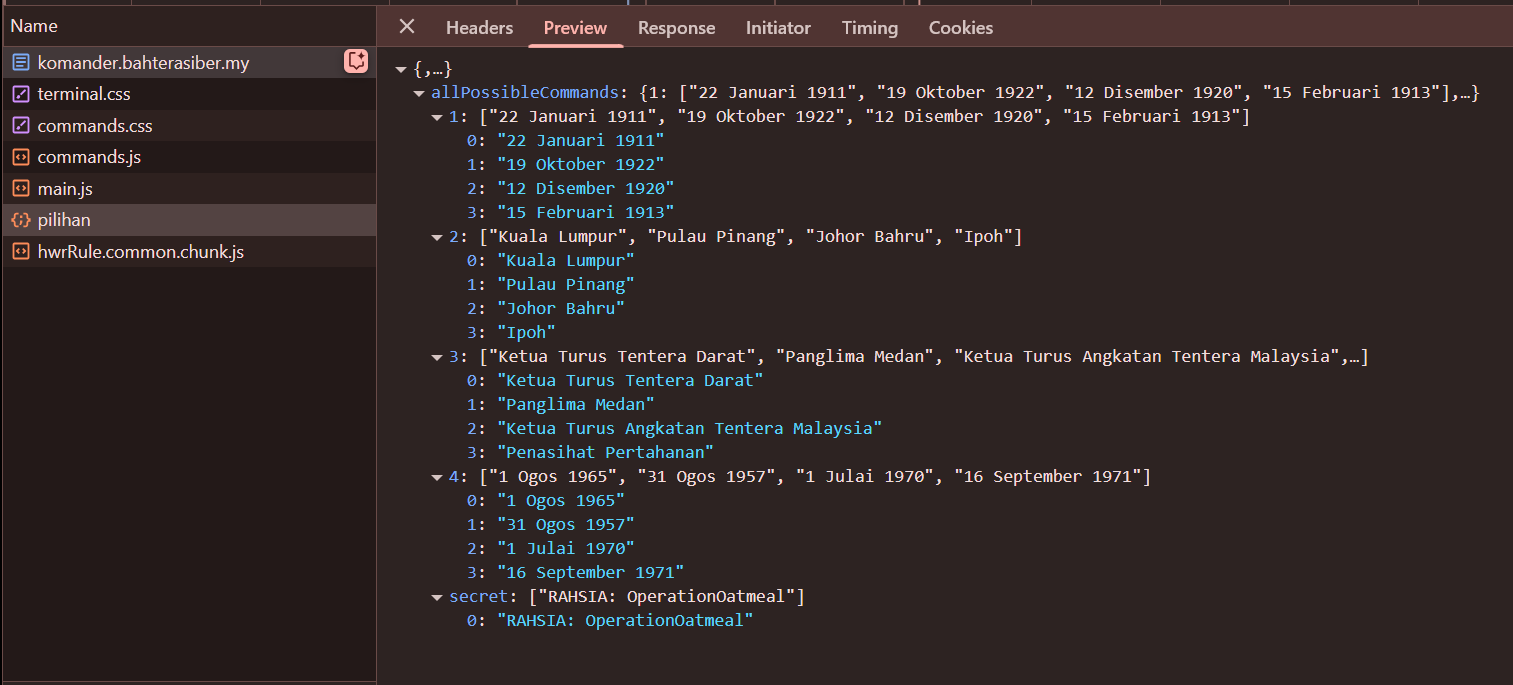
Submit the Command
Send the recovered command to /api/check as JSON:
curl -s -X POST http://<TARGET>/api/check \
  -H "Content-Type: application/json" \
  -d '{"command":"RAHSIA: OperationOatmeal","step":1}'
Flag
3108{0p3R4T10n_O@Tm34l_1bR4h1M_1sM@1L}Related Writeups

Authorized security practice only. These notes are for lab, CTF, and explicitly permitted environments.